
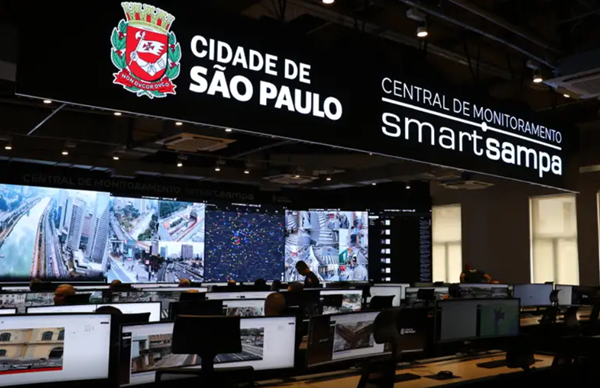
On Tuesday, October 20, 2026, an investigative report by UOL revealed that restricted data from Smart Sampa remained exposed in a public online repository for approximately 11 months. During this period, the safety and privacy of millions of people were left vulnerable. Smart Sampa is the São Paulo municipal government’s video surveillance program, integrating roughly 58,000 cameras across the city. The report stated that confidential and restricted platform credentials were left exposed online. Using these compromised credentials, UOL accessed the platform and viewed feeds from basic health units (Unidades Básicas de Saúde – UBS), schools, daycare centers, psychosocial care centers (Centro de Atenção Psicossocial – CAPS), hospitals, and emergency care units (Unidades de Pronto Atendimento – UPA). According to the investigation, the breach enabled access to live surveillance feeds, raising sharp questions regarding data security and user access governance across an infrastructure intended for public security.
This Content Is Only For Subscribers
To unlock this content, subscribe to INTERLIRA Reports.
Scale of the Breach and Risks to the Public
The compromised materials included 181 usernames and passwords of authorized personnel, personal records of more than 6,000 security agents, and step-by-step instructions to replicate Smart Sampa access on any desktop or mobile device. UOL reported viewing camera feeds across public facilities and demonstrated real-time access by filming its own reporters standing in front of municipal cameras in downtown São Paulo. While this test proved unauthorized access to the inspected cameras, it does not imply that all 58,000 cameras were accessed or that archival footage was broadly exfiltrated. Nevertheless, the ability of unauthorized third parties to monitor individuals, vehicles, and facilities creates critical vulnerabilities, including illicit tracking, routine mapping, and compromised movement security. The news reports, however, presented no evidence that criminal actors exploited this data for malicious purposes.
City Hall Blames Civil Servant and Announces Countermeasures
When questioned, the São Paulo City Government asserted that there were no vulnerabilities within the Smart Sampa platform’s technical security architecture. According to municipal authorities, the incident resulted from an illegal data leak perpetrated by an individual civil servant among more than 7,500 security personnel. The employee was identified, suspended, and is currently under investigation by the Internal Affairs Department of the Metropolitan Civil Guard (Corregedoria da Guarda Civil Metropolitana). On October 27, the mayor also announced a mandate requiring facial recognition verification for all municipal employees logging into the system. While this countermeasure is designed to prevent third parties from utilizing stolen credentials, identifying the individual responsible for the leak does not, on its own, clarify why the repository remained publicly accessible for months, nor does it confirm whether existing security mechanisms were capable of detecting and mitigating unauthorized access.
Expanded Data Sharing Requires Commensurate Controls
On Tuesday, October 27, the São Paulo City Government and the São Paulo State Public Prosecutor’s Office (Ministério Público – MP-SP) executed two data-sharing agreements regarding the Smart Sampa camera network. One agreement allows the Special Action Group for Combating Organized Crime (Grupo de Atuação Especial de Combate ao Crime Organizado – GAECO) to leverage the system during criminal investigations. The second agreement utilizes camera feeds to locate individuals accused of domestic violence who have yet to be served with court-ordered protective measures. While these initiatives expand the system’s investigative utility, they heighten the urgency for granular access controls, immutable audit trails of user activity, and automated behavioral monitoring to identify activity that exceeds legitimate job responsibilities.
Analysis
The Smart Sampa data leak demonstrates that the security of large-scale surveillance platforms depends as much on user access management and internal governance as on underlying software architecture. Even when leaks originate internally, exposed credentials can turn a tool meant for public defense into a vector for corporate and public vulnerability.
For organizations that manage proprietary camera networks or share video feeds with public monitoring hubs, the primary takeaway is the necessity of rigorous access rights management, auditable search trails, and swift incident-response capabilities. Robust multi-factor authentication, regular access credential audits, and continuous monitoring are indispensable components of a security posture designed to isolate breaches rapidly and protect the privacy of monitored individuals.

